Supabase Blog first-party post · Published 2026-08-24
Supabase adds centralized access management for Claude
Supabase’s enterprise-managed authorization lets an admin approve the Claude connection centrally while members keep their existing Supabase roles and project permissions.
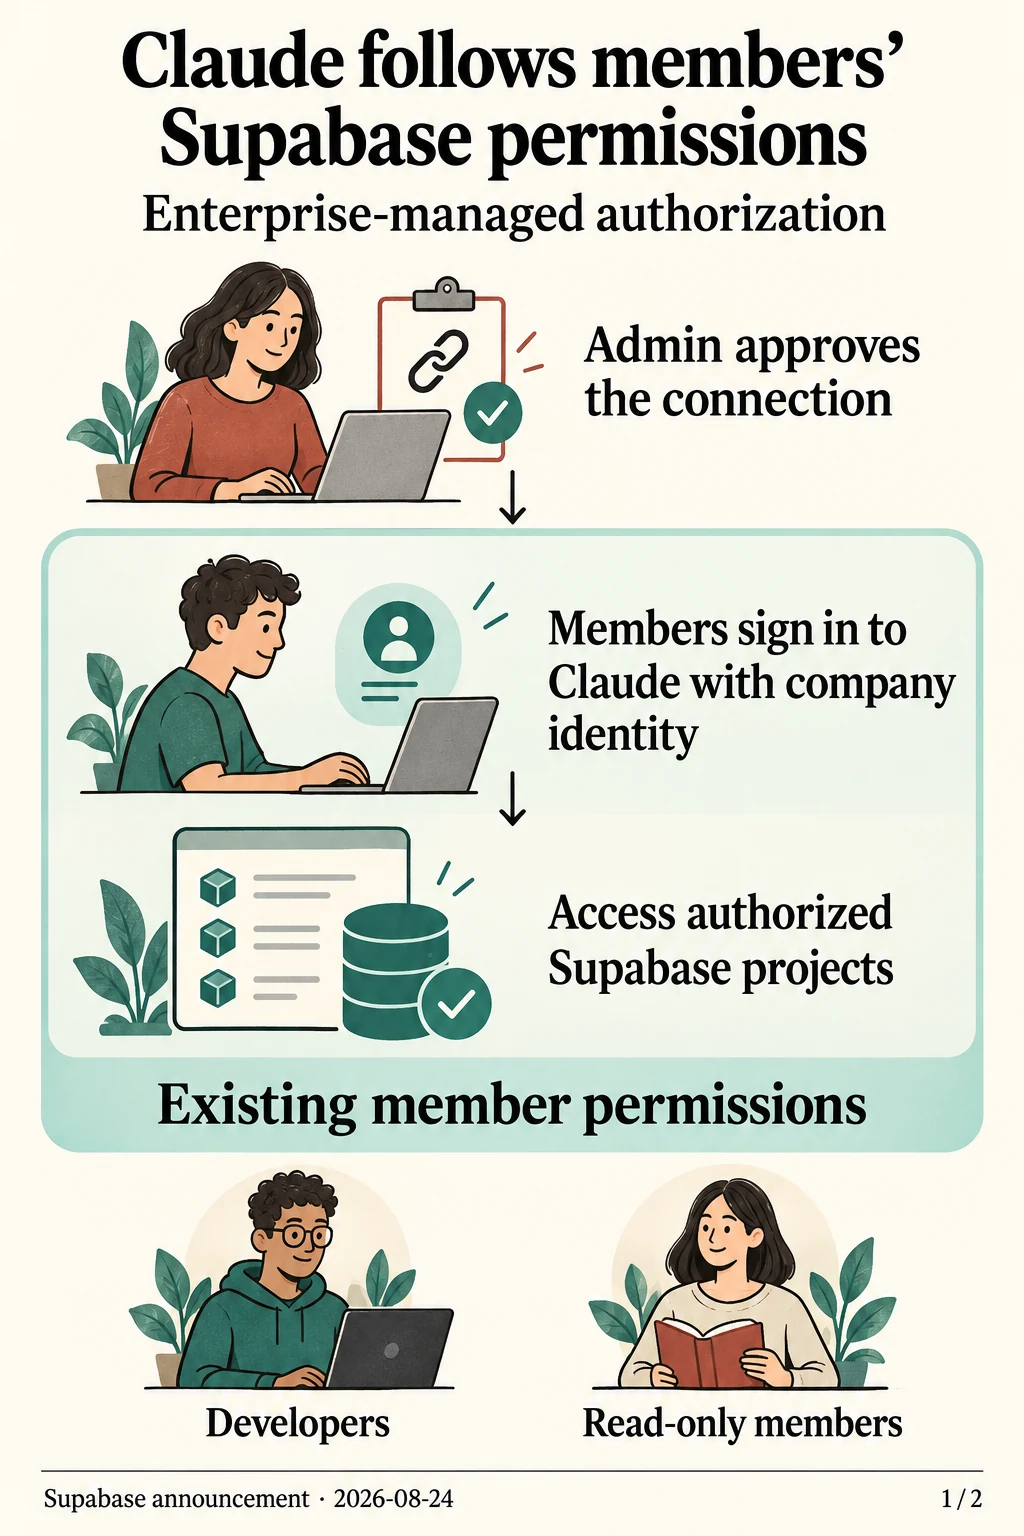
Approve centrally, retain member permissions
Supabase’s August 24 announcement describes central approval of the Claude connection. Members sign in with company identity and retain their existing Supabase roles and project access, including developer and read-only roles.
Plan and configuration requirements
The announced setup requires Team or Enterprise plans on both Supabase and Claude, with Okta SSO configured.
The documentation checked on September 9 requires ID-JAG support from the identity provider and explicit MCP-client authorization by an organization owner. Configuring the issuer alone does not grant client access. Requests remain within existing member permissions; the announcement lists SCIM provisioning as a future plan.
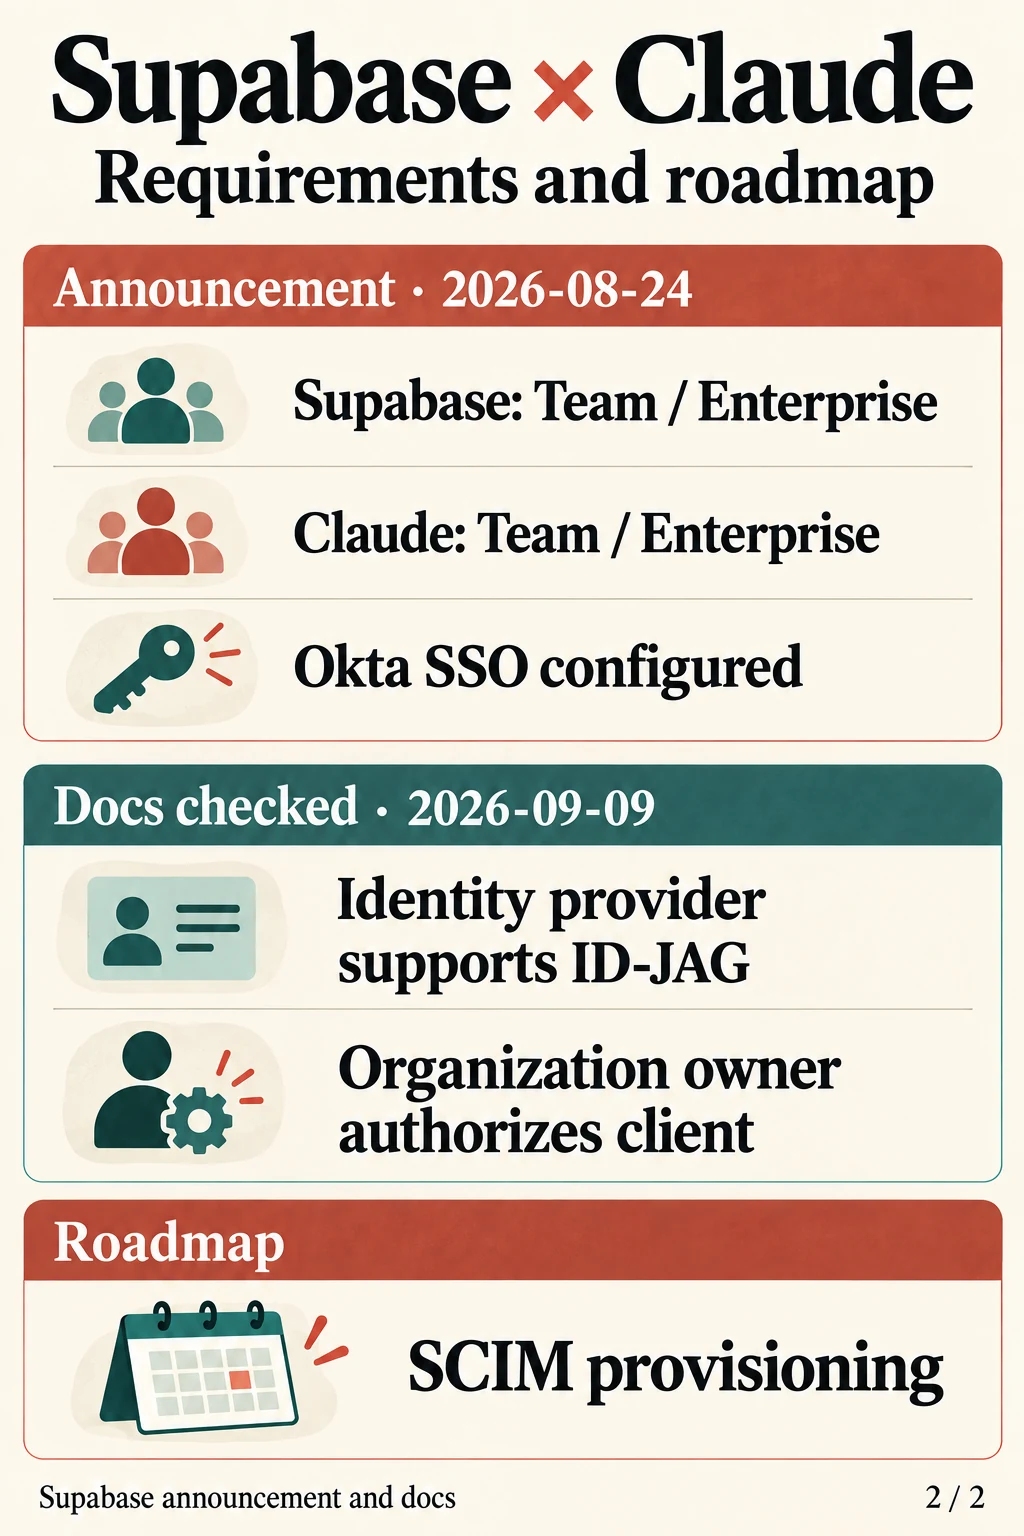
Important additions and corrections
Dates below mark changes to our coverage.
- Addition ·
Added the plan and identity requirements for managed authorization: SSO alone is insufficient; ID-JAG support and explicit client authorization are required.
Sources and notes
sources中文
Sources and notes
- Read the originalSupabase Blog first-party post
- Supabase enterprise MCP authentication documentation
Retained summary and context
Teams with managed identity can let Claude project access follow employees’ existing Supabase permissions.
SSO alone is insufficient: current docs also require an identity provider supporting ID-JAG and explicit client authorization. Plan and client requirements apply. SCIM remains planned, and we have not tested costs or management outcomes.
Sources and evidence · 4 links
Each link has a purpose and scope. Link counts do not establish independent confirmation; direct support applies only to the statements specified below.
- Supabase Blog first-party postDirect support
Read the August 24 GA announcement and current setup docs, distinguishing the announced Claude/Okta/plan combination from general protocol requirements. Checked inherited permissions, ID-JAG, client authorization and the SCIM roadmap.
Limits: No live organization was connected, and authorization, revocation, cost and time savings were not tested. Documented conditions do not imply support across all MCP clients.
- Supabase enterprise MCP authorization documentationDirect support
Currently documented plans, ID-JAG, owner authorization and token behavior.
Limits: No pinned publication date; not proof of identical wording on August 24.
Claude-side Supabase integration and June publication/August GA-update context.
Limits: An older beta paragraph remains; the dated top update supports GA. This is not independent outcome verification.
Source timeline
- · Found this reading link via Supabase Blog.
Collection record
First discovered:
Collection and source publication have distinct dates.
Editorial record
Sources reviewed
· Beijing time (UTC+8)
Reviewed official materials to clarify purpose, changes and usage conditions, distinguishing source descriptions from untested results. Original publication and observation dates are retained; an editorial revision is not a new product release.
Sources and full record
This dates our review of the wording and sources, not a project release or product update.
- Official Supabase MCP GA announcement
- Supabase enterprise MCP authorization documentation
- Claude enterprise-managed auth announcement and GA update
- Retained publication and discovery entry