Anthropic official docs via the AlphaSignal daily · Published 2026-08-25
Claude managed access: company login, fewer prompts
Employees can use configured Claude connectors through their existing corporate login, with fewer consent screens. Identity and authorization services still validate credentials and enforce company access policies.
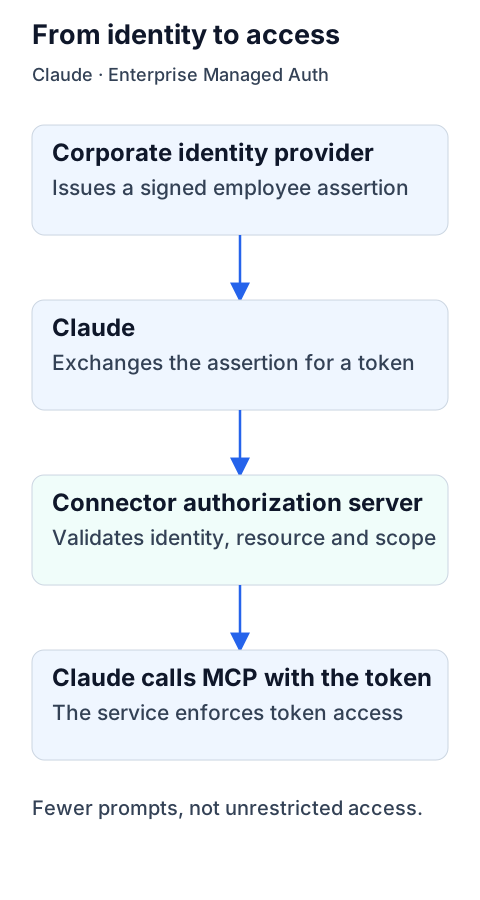
From corporate login to connector access
The documentation lists Team and Enterprise support. An administrator configures the identity provider and connector. Claude obtains a signed assertion for the employee and exchanges it at the connector’s authorization server for an access token. The MCP server still receives a bearer token; the browser redirect and consent page disappear.
The identity provider identifies the employee. The authorization server validates that assertion and maps it to resources and access scope. These roles may belong to different tenants of one identity platform. Enabling a connector does not grant every employee unrestricted data access.
Requirements and token renewal
The connector needs MCP authorization and resource discovery. Its authorization server must support the JWT bearer grant and recognize Claude’s registered client identity. Dynamic Client Registration is unsupported. Each tenant needs trusted issuers and full assertion validation.
The authorization server sets access-token lifetimes; the identity provider sets assertion lifetimes. Existing corporate-session credentials can support renewal without another login. Protected calls returning 401 can trigger silent authorization and retry. Fully unauthenticated servers do not use this flow. Availability depends on configuration and support across the participating services.
Important additions and corrections
Dates below mark changes to our coverage.
- Correction ·
Added identity assertions, tokens, tenant access and integration requirements; withdrew an unsupported regional availability generalization.
Sources and notes
sources中文
Sources and notes
- Read the originalAnthropic official docs via the AlphaSignal daily
- MCP Enterprise-Managed Authorization extension
Retained summary and context
Requires a Team or Enterprise plan and configuration across the organization, identity platform and connector. Silent authorization still validates identity and access; the current flow does not support DCR.
Sources and evidence · 3 links
Each link has a purpose and scope. Link counts do not establish independent confirmation; direct support applies only to the statements specified below.
Source timeline
- · Found this reading link via AlphaSignal daily.
Collection record
First discovered:
Collection and source publication have distinct dates.
Editorial record
Corrected
· Beijing time (UTC+8)
Added identity assertions, tokens, tenant access and integration requirements; withdrew an unsupported regional availability generalization. Event, discovery and collection dates remain unchanged.
Sources and full record
This dates our review of the wording and sources, not a project release or product update.
Full record: before, after and sources (JSON)